
Coinbase denied suffering a security breach Wednesday after an incident at an analytics vendor exposed some customers’ contact information.
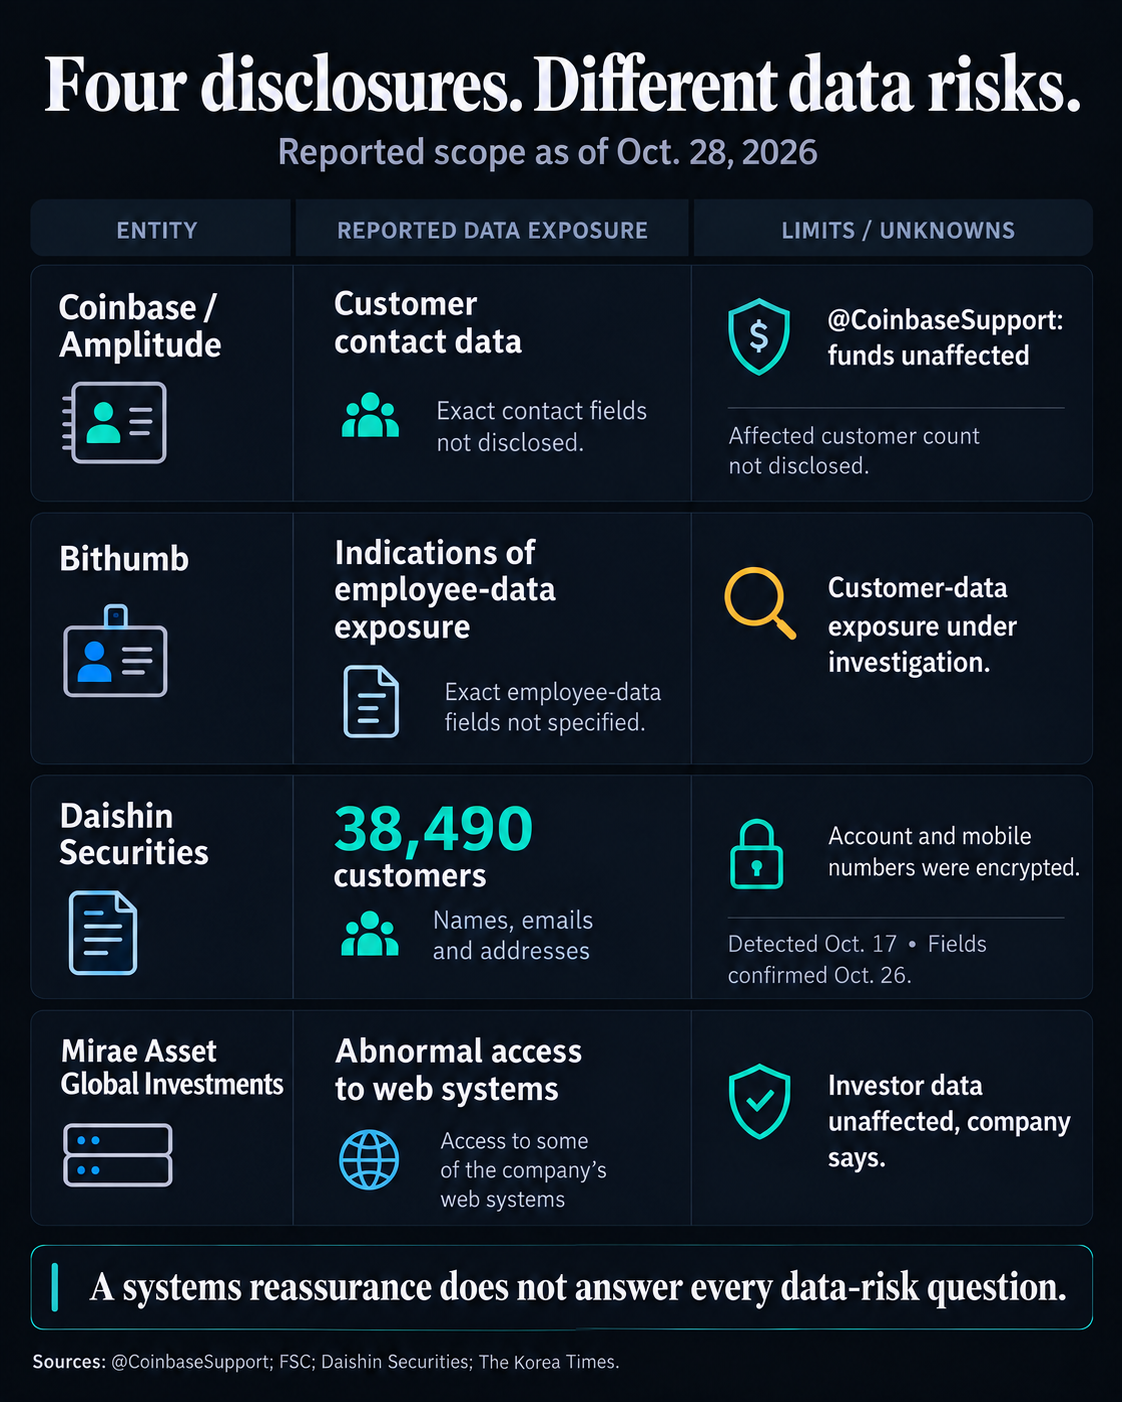
In an Oct. 28 post on X, the exchange said the incident involved Amplitude, a third-party analytics provider, and affected a small subset of its customers. It found no evidence of unauthorized access to Coinbase systems and said customer funds remained secure.
The disclosure coincided with separate cyber incidents involving South Korean cryptocurrency exchange Bithumb, Daishin Securities and Mirae Asset Global Investments, prompting Binance founder Changpeng Zhao to warn about the growing risks of exposed financial information.
“4 data leaks reported today,” Zhao wrote on X, identifying the companies before outlining how criminals exploit compromised customer records for phishing, SIM swapping and social engineering.
“You can’t prevent a leak, but you can protect yourself,” he added.
Coinbase said it was notifying affected customers and regulators but did not disclose how many individuals were involved or which contact details were compromised.
South Korea investigates breaches across financial institutions
South Korean authorities launched investigations Wednesday after Bithumb, Daishin Securities and Mirae Asset reported unauthorized access to their systems.
Daishin confirmed that personal and financial information belonging to 38,490 customers had been exposed following suspicious activity detected on Oct. 17.
The compromised records included names, email and residential addresses, login IDs, bank names and encrypted account and telephone numbers. The brokerage said it had found no evidence of unauthorized access to its core operating systems or subsequent misuse of the information.
Meanwhile, Bithumb reported that attackers accessed an internal employee communications system, exposing information involving staff, subsidiaries and business partners.
The exchange is investigating whether attackers also compromised customer records. South Korea’s Financial Services Commission said it had not confirmed any exposure of wallet addresses or information that could enable fraudulent cryptocurrency transfers.
Mirae Asset Global Investments separately detected unauthorized access to internal web systems but maintained that investor information and sensitive financial records were unaffected.
The disclosures prompted an emergency regulatory meeting and on-site investigations, extending a series of cyber incidents that had previously affected 16 South Korean financial institutions.
CZ warns of targeted phishing as crypto data breaches mount
The incidents follow several security breaches involving cryptocurrency service providers this year, including Israeli crypto broker Bits of Gold and hardware wallet manufacturer Trezor.
In August, Bits of Gold disclosed unauthorized access to its analytics infrastructure that potentially exposed customer names, contact information, Israeli identification numbers, bank details and public wallet addresses.
Trezor also reported a breach involving shipping provider ShipMonk, which exposed customer names, telephone numbers and delivery addresses.
A separate September incident involving Trezor’s email provider, Brevo, resulted in the export of 347,149 marketing email addresses and the distribution of fraudulent messages attempting to obtain wallet recovery phrases.
The incidents have intensified concerns about attackers exploiting information obtained outside exchanges’ core trading and custody systems.
Zhao warned that leaked addresses combined with cryptocurrency holdings data could expose investors to physical extortion and robbery, alongside online account attacks.
He recommended using separate email aliases and phone numbers for exchange accounts, replacing SMS authentication with passkeys or hardware security keys, and enabling withdrawal restrictions.
He also urged customers to regularly review account sessions and API permissions and distrust unsolicited messages from purported exchange support representatives.


Be the first to comment